
UK Government: Critical National Infrastructure Migration
How a UK Government department maintained availability and optimised deployment safety by securely adopting Public Cloud

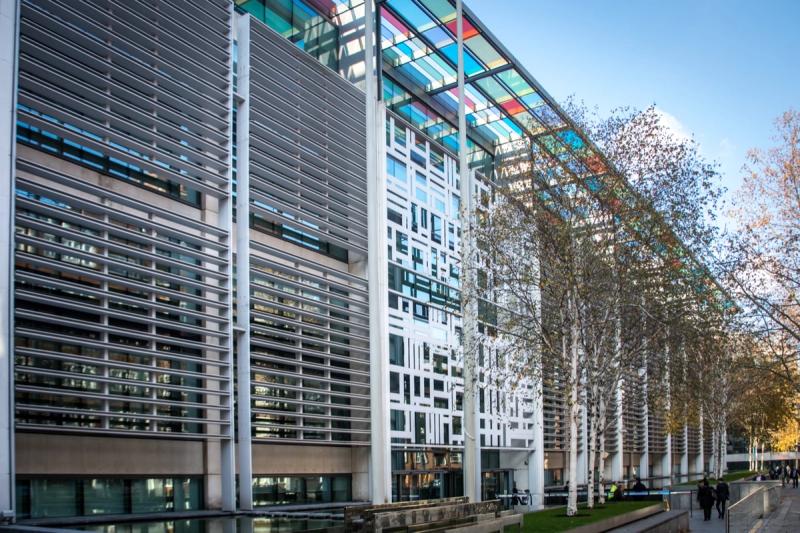
About UK Home Office
The Home Office is a United Kingdom government department responsible for overseeing immigration, law enforcement, security, and counterterrorism efforts within the United Kingdom. With a mission to keep the country safe and secure, the Home Office plays a crucial role in ensuring the integrity of the nation's borders, managing immigration processes, and maintaining public safety.
Critical National Infrastructure
The UK Home Office sought to leverage the benefits of Kubernetes and public cloud for development environments and IT operations, whilst ensuring data sovereignty and security as data centres opened in the United Kingdom. However, the recency of the technologies coupled with strict governance and compliance regulations required studious management of risk throughout the project to ensure security controls were not lost or bypassed throughout the migration process.
A central government department in the UK was responsible for a critical national infrastructure (CNI) project. The project was complex and had many stakeholders, and it had been delayed for many years. The project was also very public, and there was media coverage about the delays.
Challenges
The Home Office needed to rapidly and securely adopt public cloud. The project faced several challenges, including:
- Difficulty adopting cloud native security and DevSecOps principles within the existing methodologies of a central government department
- Lack of Kubernetes security expertise in the organisation due to recency of the orchestration technology
- Need to comply with robust government security standards for CNI
- Many stakeholders and significant media coverage
- Unquantifiable existing controls, making it challenging to assess the security posture accurately
- Managing and educating stakeholders to update existing methodologies and controls
Solutions
ControlPlane led a team that implemented a comprehensive set of solutions, including:
- Generation of a threat model and security architecture to identify potential vulnerabilities and define necessary security controls
- Introduction of vulnerability scanning, code signing, and physical hardware tokens (with the adoption of yubikeys) within pipeline and development environments
- Migration of development environments from virtualized infrastructure to the public cloud, enabling scalability and flexibility while ensuring security
- Establishing a technical risk register for the program, enabling further elements of cloud adoption on a risk managed basis
- Implementation of security controls and guardrails based on the assessed results from the threat model, mitigating identified risks
- Deployment of hardware isolation infrastructure in air-gapped environments to enhance security and protect the most sensitive systems
Business Outcomes
ControlPlane's solutions had a significant impact on the project, yielding the following outcomes:
- A 50% reduction in deployment failures and rollbacks, leading to improved project timelines and increased development velocity
- Instigation of robust DevSecOps principals, pipelines, and guard rails to ensure the usability and longevity of security controls
- Elimination of code fixes and hot patches through better test environments, developer feedback mechanisms, and uniform deployment of standardised infrastructure-as-code techniques
- Faster and more responsive engagement with Technical Design Authority and Security Assurance Board
ControlPlane's expertise with DevOps practices and container security delivered secure and efficient development and deployment infrastructure for critical national infrastructure.
Get in touch
- [email protected]
- London, NYC, Melbourne, Auckland
Related case studies
View allVerisign: Security Assurance of Critical, Internet-Scale, On-Premises Kubernetes Platform
How a global DNS and internet infrastructure provider fortified their security posture through comprehensive security assessment
LMAX Group: Cloud Native Threat Modelling and Purple Teaming
How a regulated global financial technology company that operates institutional FX and digital asset exchanges validated its cloud detection capabilities and upskilled its security engineering team through targeted threat simulation.
Questrade, Inc: GKE Infrastructure Threat Modelling
How an online brokerage enhanced the security of their GKE infrastructure to support their successful banking licence application
Speak to an expert
Engage with world-leading AI and cloud security specialists