
An evening of network security

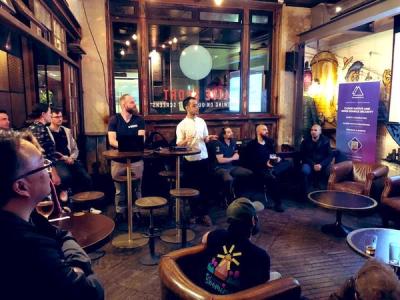
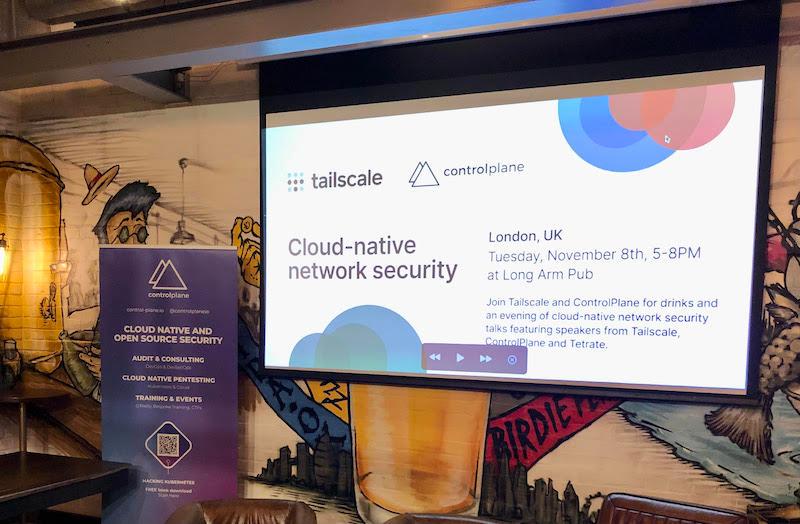
On Tuesday 8 November, we welcomed members of the Tailscale (opens in a new tab) team to London, where we enjoyed an evening of conversation around network security at The Long Arm Pub on Worship Street.
Talk 1
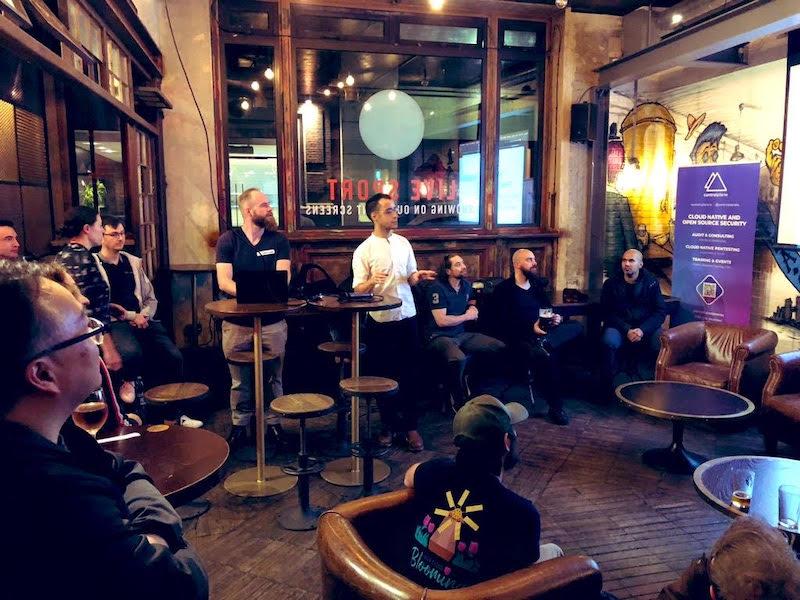
First up were Salman Aljammaz and Kristoffer Dalby of Tailscale, who told us "Why I Love DNS".
This often-overlooked protocol has had surprisingly few updates in its lifetime, and the duo went in-depth covering not only the well-known A and CNAME records, but explaining how DNAMES work, and discussing upcoming RFCs for further DNS changes.
Talk 2
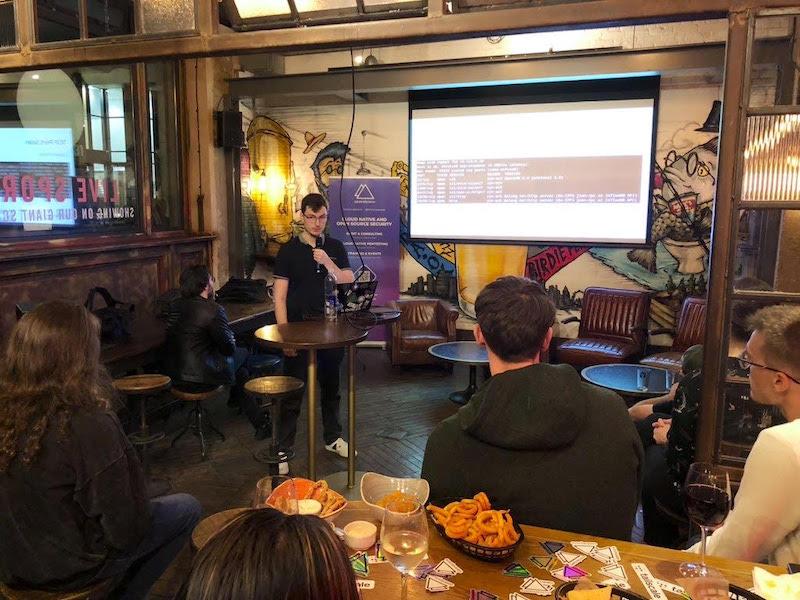
Next, our own James Cleverley-Prance explained - and demonstrated - "Three Surprising Kubernetes Networking 'Features' - And How To Defend Against Them". These non-obvious and counter-intuitive behaviours were both explained and demonstrated, and are worth knowing about. You can watch this talk online (opens in a new tab) from KubeCon EU 2022.
Panel Discussion
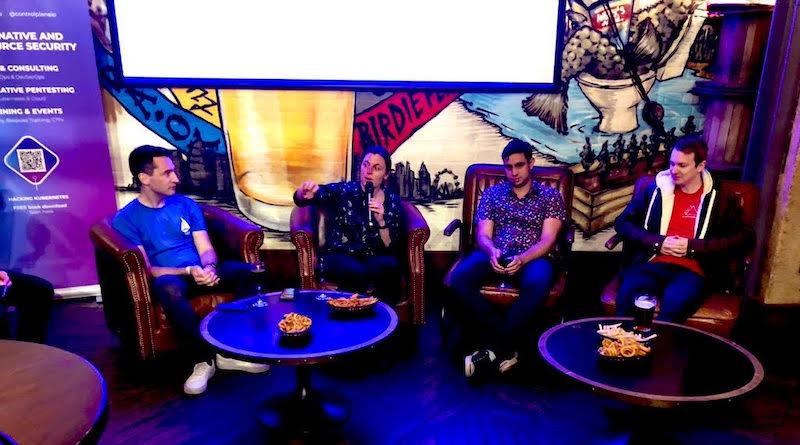
Finally, Maya Kaczorowski of Tailscale's Product Team moderated a panel discussion on cloud-native network security, with contributions from software developers Matt Turner of Tetrate, Tom D'Netto from Tailscale, and Security Architect Dr James Callaghan from ControlPlane.
The topics here ranged from the introductory "So what is cloud-native security?" to tales, tips and advice from each of the contributors' experiences, and was a great way to round-off the evening.
Our thanks to the awesome Tailscale team for a fun evening - we're already looking forward to the next one!
Want to see more talks like this? Join Service Mesh London (opens in a new tab) on Meetup.
If you'd like to see how we can help harden your network security in Kubernetes and cloud drop us a message (opens in a new tab) for a free consultation
Get in touch
- [email protected]
- London, NYC, Melbourne, Auckland
Related blogs
View allOn the Path to Gitless GitOps: Introduction
An introduction to Gitless GitOps and why you should care about it.
Old is always new - What if Hugging Face used common k8s hardening?
A critical analysis of the Hugging Face and OpenAI Agentic Intrusion through the lens of an experienced SOC Security Engineer and pentester.
Agentic Identity with OpenBao
Why AI agents require dedicated workload identity.
Speak to an expert
Engage with world-leading AI and cloud security specialists