
Securing the Kubernetes Supply Chain: Software Factory Reference Architecture

TL;DR: see our Software Supply Chain Security offering.
Watch the embedded video (opens in a new tab)
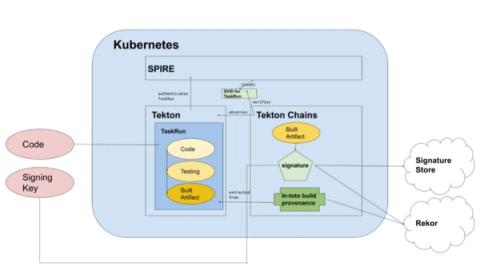
"Kubernetes Supply Chain Security: The Software Factory" explores the sophisticated mechanisms and best practices that ensure the integrity and security of software build environments. This session is tailored for security architects, DevOps professionals, and IT leaders aiming to enhance their defenses against the most cunning and disruptive cyber threats.
There is an urgent need for robust security measures in supply chain environments. Identifying vulnerabilities within the software supply chain is a wide-ranging and complex undertaking, and this session provides a comprehensive overview of the strategies and tools to mitigate these risks.
Adopting a layered security approach, incorporating automation, and utilizing open-source tools to maintain the integrity and security of software production is paramount.
Key Takeaways:
- Deep Dive into Supply Chain Threats: Understand the current threat landscape and how it specifically affects Kubernetes environments
- Best Practices and Tools: Learn about the latest tools and methodologies to secure your software supply chains effectively
- Real-World Case Studies: Gain insights from real-life scenarios where cutting-edge security practices have made a difference
For more information, please see our Software Supply Chain Security offering.
Get in touch
- [email protected]
- London, NYC, Melbourne, Auckland
Related blogs
View allOn the Path to Gitless GitOps: Introduction
An introduction to Gitless GitOps and why you should care about it.
Sovereign Signing: A Self-Hosted Supply Chain with OpenBao, Cosign, and Flux CD
A fully self-hosted software supply chain signing pipeline (OpenBao holds the key, Cosign signs, Flux CD verifies) with no public cloud KMS and no public Sigstore infrastructure.
Speak to an expert
Engage with world-leading AI and cloud security specialists