
Hack & Snack – Beer, Pizza & DevSecOps!

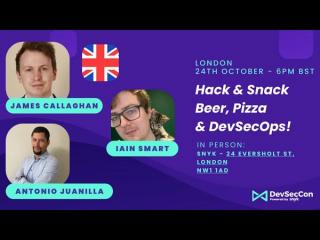
Join Us for a Fun & Casual Tech Talk Meetup!
Hosted by DevSecCon & ControlPlane at the Snyk Office on October 24th
Come for the tech, stay for the community!
Talks
I Wanna Know what Trust is - James Callaghan
From the Network to the Supply Chain
The phrase “Zero Trust” is often seen as a buzzword, or worse, as a philosophy that suggests trusting nothing and no one. In reality, Zero Trust is not about eliminating trust entirely but about eliminating implicit trust. It emphasizes the importance of establishing well-defined explicit trust relationships and performing continuous verification across all digital assets, from the core network to the extended supply chain.
This talk will explore the evolution of Zero Trust, breaking down the principles behind it and addressing the misconceptions that surround the term. We'll dive into how Zero Trust architectures can be implemented not only within networks but also throughout complex supply chains. Attendees will gain practical insights into designing security strategies that build resilient systems by "trusting, but verifying", and learn about technologies and tools which can help them implement this philosophy in their systems.
Untangling Static Pods: Navigating Kubernetes’ Hidden Edge Cases - Iain Smart
Static Pods offer a powerful but often overlooked method of running essential workloads directly on Kubernetes nodes. However, while they are essential to cluster bootstrapping, they come with their own set of challenges and edge cases that can trip up even experienced users. In this talk, we’ll explore what Static Pods are, how they differ from regular pods, and why they’re useful in specific use cases. We'll then dive in to some instances where different cluster components interact in a plethora of unusual ways, and identify some behaviours which attackers can abuse.
How attack and defend a Kubernetes cluster, intro edition - Antonio Juanilla
In this introductory session, Antonio Juanilla will explore the fundamentals of securing a Kubernetes cluster by examining both attack and defense strategies. Attendees will learn about common vulnerabilities in Kubernetes environments, as well as practical techniques to mitigate threats and safeguard workloads. Whether you're new to Kubernetes security or looking to strengthen your defenses, this talk will provide essential insights into the tools and practices needed to protect your cluster.
Related events & webinars
View allKubeCon EU London 2025 Join ControlPlane at KubeCon EU 2025
An overview of the Kubernetes security landscape, Flux CD updates, and a glance to the future 👨🚀
Is the Internet on Fire? Strategies for Mitigating Open Source Software Vulnerabilities - Andrew Martin, ControlPlane & Michael Lieberman, Kusari
Open source is deployed everywhere, but is no longer trusted by default. Supply chain attacks via package registries, GitHub, and various accidental and entirely understandable vulnerabilities have proven that nothing is entirely secure.
Insecure Execution: Attacking the Cloud Native Supply Chain with Andrew Martin
Should we trust the code we run in production? Not if a motivated attacker can compromise our system’s complex supply chains.
Speak to an expert
Engage with world-leading AI and cloud security specialists