
The ./havoc Podcast - Andrew Martin: Hacking Kubernetes

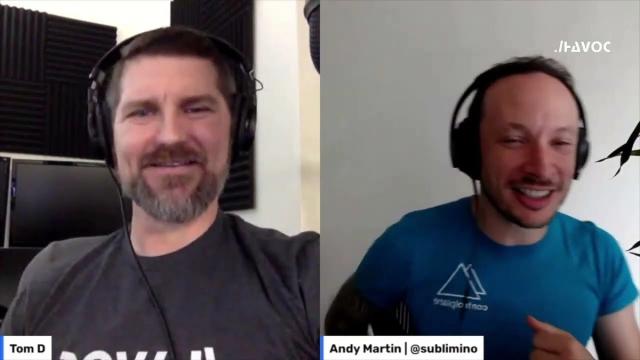
In this episode of The ./havoc Podcast Cybersecurity Research series, Andrew Martin, co-author of Hacking Kubernetes (O'Reilly Media, Inc. ISBN: 9781492081739) provides an in-depth look into how his experience advising clients on securing production Kubernetes clusters resulted in a comprehensive and masterfully written book that any CISO, Security Engineer or Incident Responder responsible for securing and monitoring Kubernetes should not go without.
Hacking Kubernetes book
OpenUK
OpenSSF
The Linux Programming Interface
Andrew has an incisive security engineering ethos gained building and destroying high-traffic web applications. Proficient in systems development, testing, and operations, he is comfortable profiling and securing every tier of a bare metal or cloud native system, and has battle-hardened experience delivering containerised solutions to enterprise and government. He is a co-founder at ControlPlane ( Andrew has presented at international conferences including KubeCon, Velocity, SANS, OWASP, DevOpsDays, Container Camp, IPExpo, and numerous other local events and meetups.
00:00 Start
00:52 Andy's background and book motivations
05:20 Piracy for the win!
07:15 Taking up the mantle of the CISO
11:20 Let's talk about Threat Modeling
20:40 Escaping containers
25:39 Linux fundamentals
31:31 Hard multitenancy
36:17 Open source IDS
39:39 One take away (or maybe three takeaways)
44:27 Rapidfire round
49:11 Wrap up
Podcast recording
Related events & webinars
View allEnvoy Gateway End User Threat Model Report: Raising Awareness of Gateway API Security - James Callaghan & Torin van den Bulk, ControlPlane
As we embrace the proliferation of microservice-based architectures in the cloud-native space, and DevOps teams face the challenge of choosing between many similar technologies, simplicity in setup and configuration becomes paramount.
Harnessing the Power of OSCAL: A Dive into Continuous and Automated Compliance for Kubernetes
Join us on a deep-dive journey through Kubernetes as we unmask the power of automated continuous compliance.
Hacking & Defending Kubernetes Clusters: We'll Do It LIVE!! - Fabian Kammel & James Cleverley-Prance
Ever wondered about the security of your own Kubernetes cluster, but new to Kubernetes security and not sure where to start?
Speak to an expert
Engage with world-leading AI and cloud security specialists