
native.cloud: Cloud Native Infrastructure Metadata Ontology

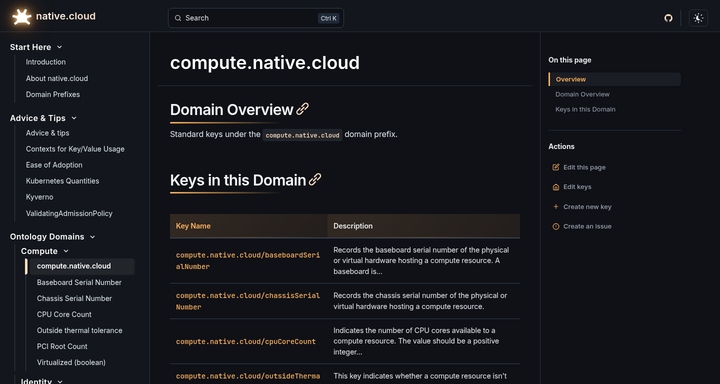
Every platform team invents its own metadata. One cluster labels a workload env: prod, the next uses environment: production, and the policy engine, cost report and incident tooling each expect something different. native.cloud (opens in a new tab) is an open ontology of shared keys for that metadata, so the same idea gets the same name across teams, tools and vendors.
ControlPlane sponsors native.cloud. The idea dates from 2020 and the site went live in 2026. The ontology is public, vendor-neutral, free to use, and licensed under CC BY 4.0 (opens in a new tab).
How It Works
Each key lives under a domain prefix and is defined once, with its meaning, the contexts it is valid in, a validation constraint and example values. You use the keys in your existing infrastructure code:
metadata:
  labels:
    workload.native.cloud/businessCriticality: critical
    workload.native.cloud/environmentName: production
Each key lists where it applies: Kubernetes labels, annotations and taints, ResourceClaims, and OCI image annotations. The site also covers enforcing keys with Kyverno and ValidatingAdmissionPolicy.
Ontology Domains
The first release defines keys across eight domains:
- compute.native.cloud: hardware, microarchitecture and virtualisation, such as CPU core count and chassis serial number.
- identity.native.cloud: operational identity and human actors, such as username and minimum remaining certificate validity.
- network.native.cloud: network topology and interface configuration, such as MAC address.
- storage.native.cloud: storage tiering and retention, such as retain-until and eligible-for-deletion-after dates.
- tenancy.native.cloud: tenant identity, tenancy model and tier, and suspension status.
- topology.native.cloud: physical location and fault domains, such as continent, country code and zone ID.
- vendor.native.cloud: manufacturer and product identifiers, such as PCI and USB vendor IDs and SLA URLs.
- workload.native.cloud: business criticality, environment, version, responsible teams, and links to dashboards, documentation and source code.
Adopt Only What You Need
native.cloud is a voluntary standard. It sits alongside the conventions you already use, rather than replacing them, and the advice is plain: don't add keys you have no use for. If a key you need is missing, propose it through an RFC on the GitHub repository (opens in a new tab).
native.cloud
The open ontology of shared metadata keys for cloud native infrastructure.
Explore the ontology (opens in a new tab)Related publications
View alleBPF Foundation Security Threat Model
A comprehensive threat model for eBPF-based security solutions.
NIST SP 800-233 Service Mesh Proxy Models
Security guide to service mesh proxy models for cloud-native applications.
Flux D1 Reference GitOps Architecture
A hardened reference architecture for GitOps with Flux CD.
Speak to an expert
Engage with world-leading AI and cloud security specialists