
CNCF Cloud Native Security Whitepaper

The CNCF has published a new CNCF Cloud Native Security Whitepaper (opens in a new tab), which addresses some of the security challenges in deploying a cloud native system, and offers recommendations to CISOs, architects, and developers.
ControlPlane CEO Andrew Martin and Head of Security Rowan Baker authored and contributed to sections of the document, along with numerous other community contributors and reviewers.
Some of the sections containing ControlPlane's contributions:
- Build pipeline (opens in a new tab)
- Testing and security testing (opens in a new tab)
- Threat Modelling (opens in a new tab)
Thanks to the sig-security leadership, and multitude of other authors and contributors.
Get in touch
- [email protected]
- London, NYC, Melbourne, Auckland
Related blogs
View allInternal ≠ Isolated (Or Secure): The Argo CD Repo-Server Flaw
An unpatched, unauthenticated RCE in the Argo CD repo-server that can chain into full Kubernetes cluster takeover.
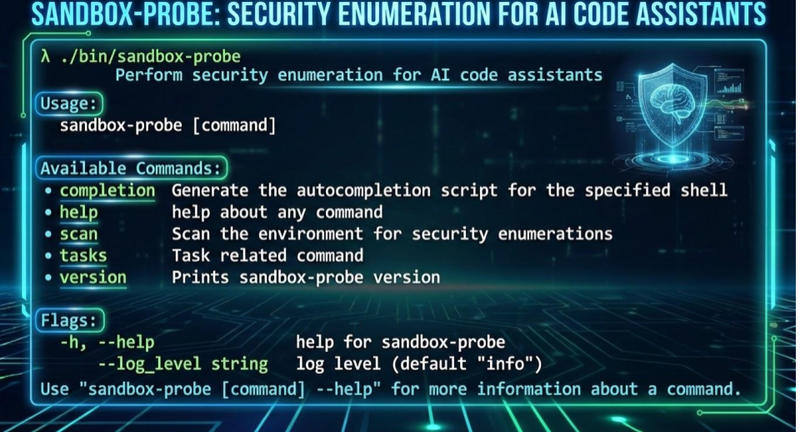
sandbox-probe: Putting AI sandboxing to the test
Announcing ControlPlane's sandbox-probe: testing the limits of AI Agent Sandboxes
ControlPlane Launches Enterprise Support For OpenBao To Strengthen Secrets Security
ControlPlane Launches Enterprise Support for OpenBao.
Speak to an expert
Engage with world-leading AI and cloud security specialists