
The Most Excellent Learnings of CloudNative SecurityCon 2023

At the inaugural CloudNative SecurityCon, ControlPlane kicked off the week’s events with a Zero Day training event in partnership with AWS and Ergonautic. We were live-breaking and securely re-building K8S and cloud native systems. To open up the day, talks were heard from Ergonauts Andrew Clay Shafer (opens in a new tab), Sasha Rosenbaum (opens in a new tab), and Jabe Bloom (opens in a new tab) on driving value change for security teams. Their framing set the tone; look at the complete picture of your system which is not only confirmed by the platform and apps, it also includes the people. From there, ControlPlane’s very own Marco De Benedictis (opens in a new tab) got technical matters into gear combining salient modules from ControlPlane’s advanced Kubernetes security, and Threat Modeling Kubernetes courses. To wrap up the day, Amazon’s Jeremy Cowan (opens in a new tab) contextualised the training by providing a detailed view on EKS security.
The event had a great turnout with prominent guests in attendance. Everyone had a lot of fun breaking, learning, and rebuilding alongside each other. ControlPlane will host further events like this one around future conferences and community events.
The first day of the conference saw keynotes featuring luminaries such as Emily Fox (opens in a new tab) (YouTube (opens in a new tab)), Liz Rice (opens in a new tab) (Youtube (opens in a new tab)), Brandon Lum (opens in a new tab), Zack Butcher (opens in a new tab) (Youtube (opens in a new tab)), Brian Behlendorf (opens in a new tab) (Youtube (opens in a new tab)), and Loris Degioanni (opens in a new tab) (Youtube (opens in a new tab)). Andy Martin (opens in a new tab) and Andres Vega (opens in a new tab) were graced by the opportunity to share the stage with such distinguished speakers that encompass the leadership of our community, to speak about “Learn by Hacking: How to Run a 2,500 Node Kubernetes CTF” (YouTube (opens in a new tab)).
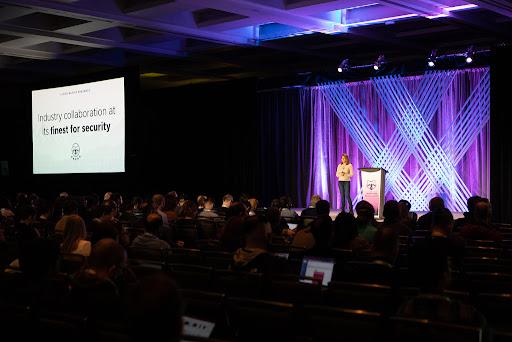
Overall, CloudNative SecurityCon was a spectacular success for ControlPlane, where through the delivery of the day-long Cloud Native Capture The Flag, we were able to help players see ahead, connect and apply what they heard from the event talk sessions, and gain practical skills to be even sharper security practitioners.
Kudos to all participants who played, including Greg Castle (opens in a new tab) and the GKE (opens in a new tab) security team, Jay Beale (opens in a new tab)(who runs the DEFCON K8s CTF (opens in a new tab) with Inguardians (opens in a new tab)), and Isovalent (opens in a new tab) Field CTO Duffie Cooley (opens in a new tab), long-time collaborator and teacher to players of the game.
Aside from the CTF, ControlPlane also led two other sessions. A threat modelling teardown session “Security Threat Modeling Live from Scratch Session” (YouTube (opens in a new tab)), and the talk “Avoiding IAC Potholes with Policy + Cloud Controllers” on OSCAL (using Kyverno, Crossplane, OSCAL, and Defence Unicorn’s Lula) (YouTube (opens in a new tab)).
And friends and peers in the cloud native security community were met and made!
As usual, swag was aplenty — especially ControlPlane's high-quality fleece-lined hoodie, incredibly warm (opens in a new tab) and perfect for the exquisite chill of Seattle winters.
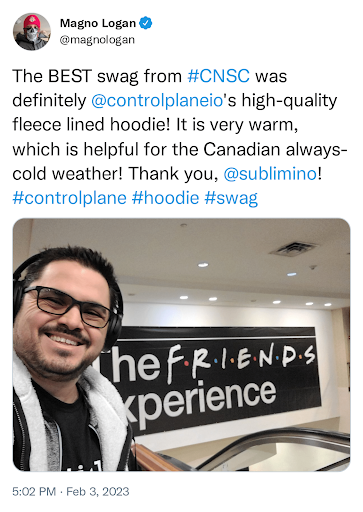
ControlPlane distributed 50lbs worth of swag to CTF winners and worthy questioners. If you feel you missed out, drop us a line and we’ll ship you some!
Huge thanks to all the hard work put in by the organisers, we look forward to the Security Village at KubeCon EU, and running another event in EMEA time. As usual, if you’re interested by our work in CNCF TAG Security (opens in a new tab) drop into a call and introduce yourself.
We’ll be a State of Open Con (opens in a new tab) in London this week! If you’d like to talk about open source and cloud native security our CEO Andrew Martin will be around. Contact us to book a chat.
Get in touch
- [email protected]
- London, NYC, Melbourne, Auckland
Related blogs
View allInternal ≠ Isolated (Or Secure): The Argo CD Repo-Server Flaw
An unpatched, unauthenticated RCE in the Argo CD repo-server that can chain into full Kubernetes cluster takeover.
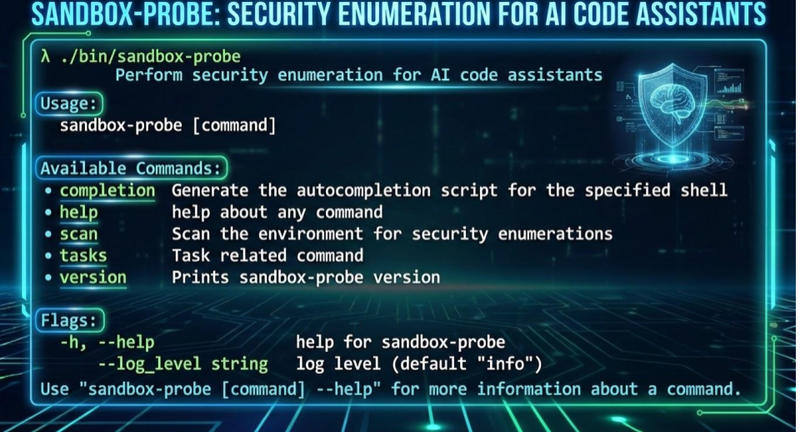
sandbox-probe: Putting AI sandboxing to the test
Announcing ControlPlane's sandbox-probe: testing the limits of AI Agent Sandboxes
ControlPlane Launches Enterprise Support For OpenBao To Strengthen Secrets Security
ControlPlane Launches Enterprise Support for OpenBao.
Speak to an expert
Engage with world-leading AI and cloud security specialists