
Smarter than your average SBOM ! | Matt Jarvis & Andrew Martin

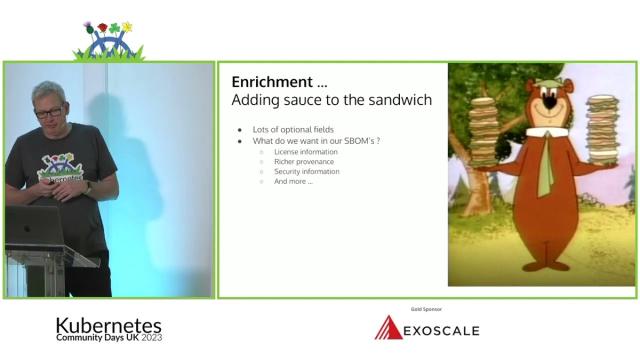
SBOM’s are the hot new thing in security topics - everyone wants one, but no-one is quite sure what they do with them. In this talk we’ll dig into the picnic baskets of the SBOM campground, hoping to uncover some tasty morsels about the emerging SBOM lifecycle. We’ll cover topics like where we should create, store and distribute them, how can we prove they can be trusted, and adding sauce to the sandwich with enrichment and companion formats. Come and join the party - Yabba Dabba Doo !
Related events & webinars
View allHack & Snack – Beer, Pizza & DevSecOps!
Hosted by DevSecCon & ControlPlane at the Snyk Office on October 24th
Is the Internet on Fire? Strategies for Mitigating Open Source Software Vulnerabilities - Andrew Martin, ControlPlane & Michael Lieberman, Kusari
Open source is deployed everywhere, but is no longer trusted by default. Supply chain attacks via package registries, GitHub, and various accidental and entirely understandable vulnerabilities have proven that nothing is entirely secure.
Invisible Infiltration of AI Supply Chains: Protective Measures from Adversarial Actors - Torin van den Bulk, ControlPlane
Malicious human and AI actors can infiltrate AI supply chains, compromising the integrity and reliability of the resultant AI systems through training data tampering, software or model backdoors, model interference, or new runtime attacks.
Speak to an expert
Engage with world-leading AI and cloud security specialists